One platform for Enterprise AI.
Deployed Your Way.
Photon is a four-layer architecture spanning experience, governance, zero-trust data, and the edge. It runs in your cloud, in your data center, or fully air-gapped behind the network boundary.
"Bring the AI to the data and the device, not the other way around."
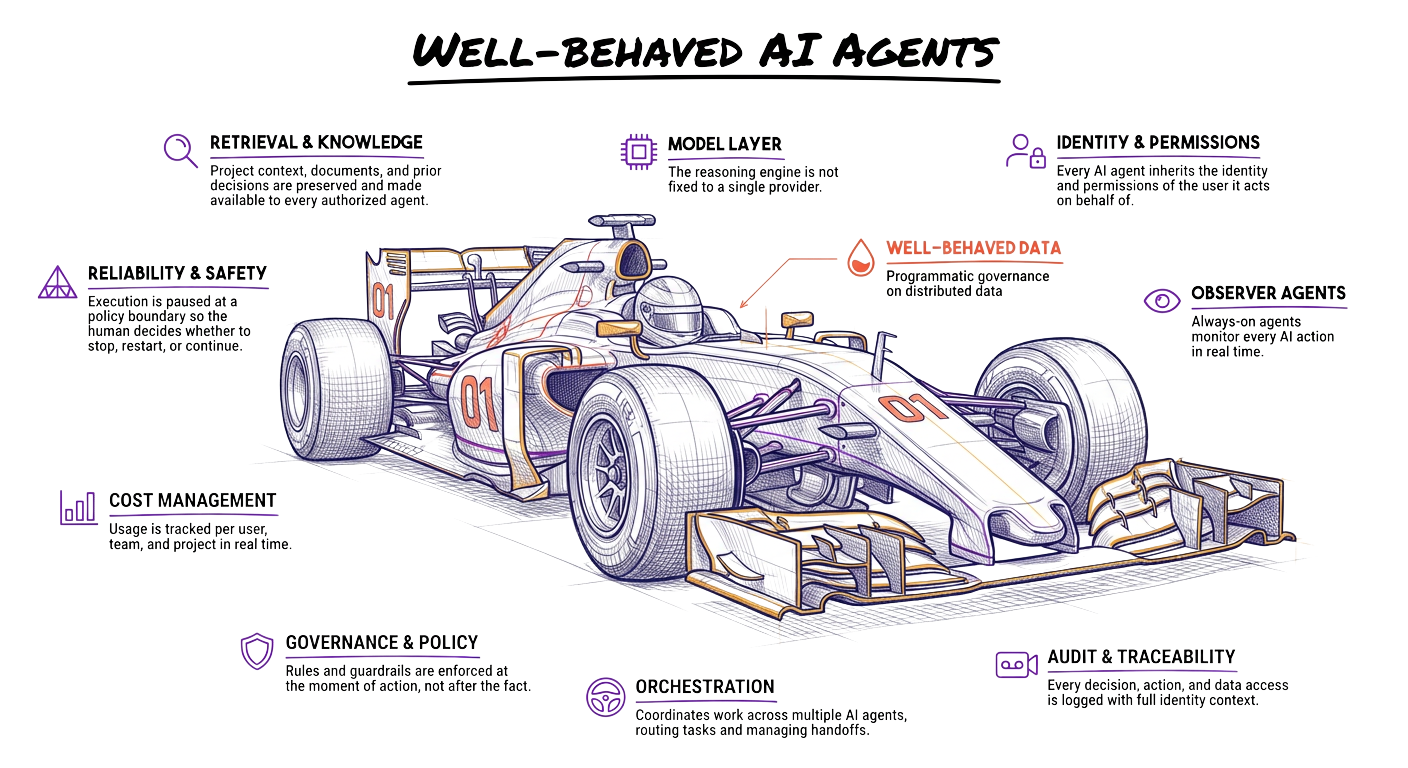
Most AI stops at the edge of your network.
Cloud-only AI cannot reach the machines, code, and sensitive data that run your operations. The most valuable work happens in environments that can't, or won't, call out to a public endpoint.
The Connectivity Gap
Factory floors, secure facilities, and field operations are disconnected or air-gapped by design. Cloud-only AI simply cannot reach them.
Data Gravity
The data that matters most is heavy, regulated, and pinned to its source. Moving it to the AI is slow, costly, and a compliance liability.
The Trust Boundary
Connecting local devices and code to AI usually means punching a hole in your security perimeter. Governance breaks down at the edge.
Four layers. One governed platform.
Each layer is a product in its own right, and together they compose a single architecture where governance and zero-trust data controls extend from the cloud all the way to the edge.
Bring AI to the Edge.
Photon Edge is the edge runtime that extends the platform to where work actually happens. It connects local devices, code, and data to Photon, carrying the same governance, identity, and audit controls as the cloud workbench.
It runs connected, intermittently connected, or fully air-gapped. The experience never changes. Only the deployment boundary does.
Desktop
Zero-trust data, everywhere the platform runs.
Data Foundations is the layer that makes every other layer safe. Agents query encrypted data in-use, with no decryption keys and no data movement. The same controls apply whether an agent runs in the cloud workbench or on a Photon Edge at the edge.
- ATOMIC ENGINE encrypts records into self-describing, policy-bearing ATOMs
- SEID lets agents query encrypted datasets with standard SQL
- PRISM enforces field-level zero-trust controls that travel with the data
- BEAMS dynamically transforms data by consumer identity and purpose
Three Deployment Models
The same platform, the same governance, matched to your environment, your data gravity, and your trust boundary.
Centralized
The full platform runs inside your environment: your VPC, your data center, or your government cloud. No external dependencies.
- Defense & Intelligence
- Single-tenant regulated enterprise
- Data-sovereignty mandates
Plugs into the stack you already run
Photon binds to your ecosystem at three layers: models, enterprise systems, and data, each governed by the same control plane.
Any model, including your own
Switch foundation models with one click. Bring private, self-hosted, and open-weight models through any OpenAI-compatible endpoint: NVIDIA NIM, Hugging Face, Ollama or vLLM. Your models, your perimeter.
Connects to the systems you run
Register any enterprise system as a governed agent over MCP. Every action is policy-checked and audited before it touches your systems of record.
Governs data in place
Query and protect data where it already lives, with no copies or extraction. SEID, PRISM and BEAMS enforce field-level zero-trust across every major warehouse.
Open to any model, system, or warehouse via MCP & OpenAI-compatible endpoints. Logos shown are representative; specific connectors are confirmed during architecture scoping.
Map Photon to your architecture.
Book a 90-minute architecture workshop. We'll map your environments, data gravity, and governance requirements to the right deployment model, from cloud to the edge.