Programmatic Control at
Agentic Speed.
Limited architectural control over Agentic AI means that mistakes have no undo. At these speeds, AI can only be governed programmatically.
Photon Runtime AI Governance protects IP and sensitive data, and reduces execution risks by enforcing zero-trust policies through code at the point of agentic execution.
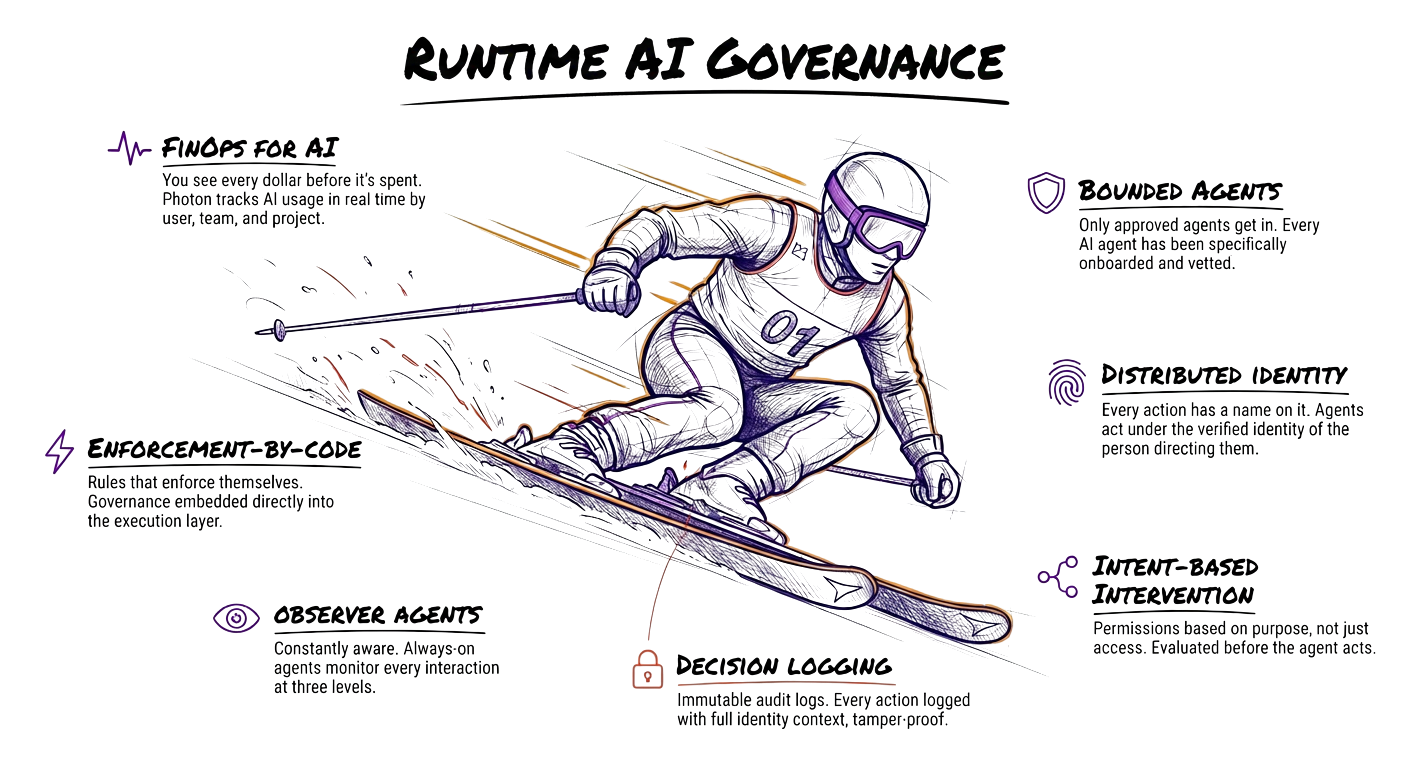
The Agentic AI Control Gap
AI agents make decisions on the fly, take unexpected paths, and act faster than any human can review. Today's governance models are built for traditional software. They need new models and new technology to suitably govern the use of strategic assets in this new era.
AI agents create scenarios you can't predict. The only way to govern them is in real time, responding to what's actually happening. At speed.
This is runtime AI Governance.
- Speed:Days / WeeksMilliseconds
- Mechanism:Static ChecklistsObserver Agents
- Context:Lost in translationCryptographically bound
Control Starts with Cost
You See Every Dollar Before It's Spent.
- AI costs become unpredictable when agents consume tokens without limits or visibility. Photon tracks usage in real time, by user, team, and project
- Auto-enforces token limits before budgets spiral, and shows you the actual value AI is generating across your organization. No surprise bills. No shadow spend.
Only Approved Agents Get In.
- Every AI agent available to your teams has been specifically onboarded and vetted by your enterprise
- No unauthorized agents, no shadow AI, no surprises.
Every Action Has a Name on It.
- No shared service accounts. No blanket access. Every agent acts under the verified identity of the person directing it
- Permissions enforced at every step, regardless of where the data lives.
Permissions Based on Purpose, Not Just Access.
- Having access to data doesn't mean you can do anything with it. Photon evaluates the purpose of every request
- Enforces permissions based on what the user is trying to accomplish, before the agent acts.
Constantly Aware.
- Observer Agents are Photon's always-on governance layer, monitoring every agentic interaction at three levels: personal, project, and enterprise
- Deviations from policy are flagged or blocked as they happen, not discovered in a quarterly audit.
Rules That Enforce Themselves.
- Prompt-based instructions are suggestions. Code-based enforcement is absolute. Photon embeds governance directly into the execution layer
- Blocking policy violations and validating agent responses against malicious or compromised inputs before they reach the user.
Immutable Audit Logs
- Transactions are logged across the entire execution chain with full identity awareness: who asked, what was requested, what was done, by whom, and under what authority.
- Every blocked action, override, and policy decision is cryptographically recorded and tamper-proof, ready for compliance review, reconstruction, and audit at any time.
- Logs are scoped by user, team, and project, giving compliance teams the granular visibility they need without sifting through noise.
Execution Interception
When runtime governance detects a policy violation, it halts execution and surfaces a Human-in-the-loop control interface.
Secure your AI workflows today.
QuantumZero tools offer controlled policy enforcement across AI agents and protection of sensitive data in-use.